

Mark E. S. Bernard, vCISO, CAIO, AI Governance Architect
vCISO & Fractional CAIO | Cybersecurity, GRC & AI Governance Executive | ISO 27001 • ISO 42001 • NIST CSF | Building Trust, Reducing Risk and Enabling Secure Growth
Executive Summary
An employee asks an AI assistant to check a supplier invoice. The assistant retrieves the supporting documents, notices a payment instruction and prepares an update to the finance system.
The instruction looks routine. It arrived inside a document the assistant was supposed to read. Yet someone changed that document to steer the assistant toward a different bank account.
At that moment, the people affected are far removed from the model: an employee trying to finish a task, a supplier waiting for payment and a finance leader accountable for the loss.
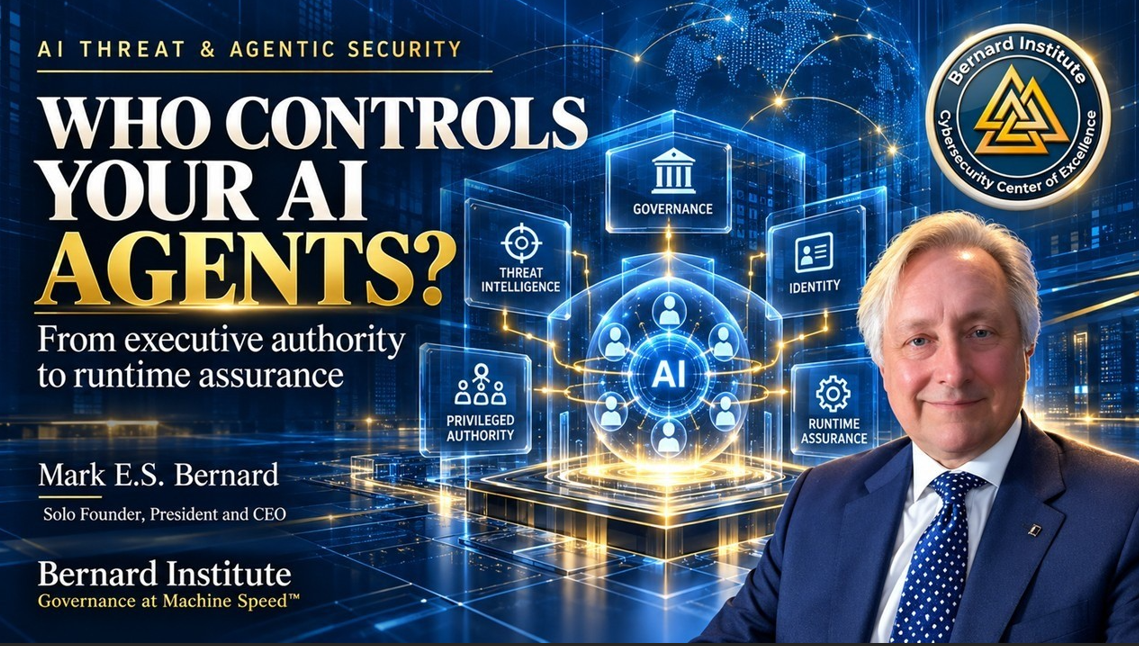
This is a hypothetical example, but it captures the problem addressed by the AI Threat and Agentic Security Reference Architecture. Once an AI system can use tools, change records or delegate work, its security depends on the authority it receives and the boundaries around each action.